Every business sending sensitive prompts to an AI model wants the same three answers. Where does the data live. How long does it stay there. And what, if anything, gets done with it. Two of the biggest AI labs just gave two different answers in the same week, and the gap between them says more about how AI privacy actually works than either announcement does on its own.
What changed at Anthropic:
- Since June, businesses on Claude Fable 5 had to accept 30 days of Anthropic holding their conversations, a rule that pushed some customers away entirely
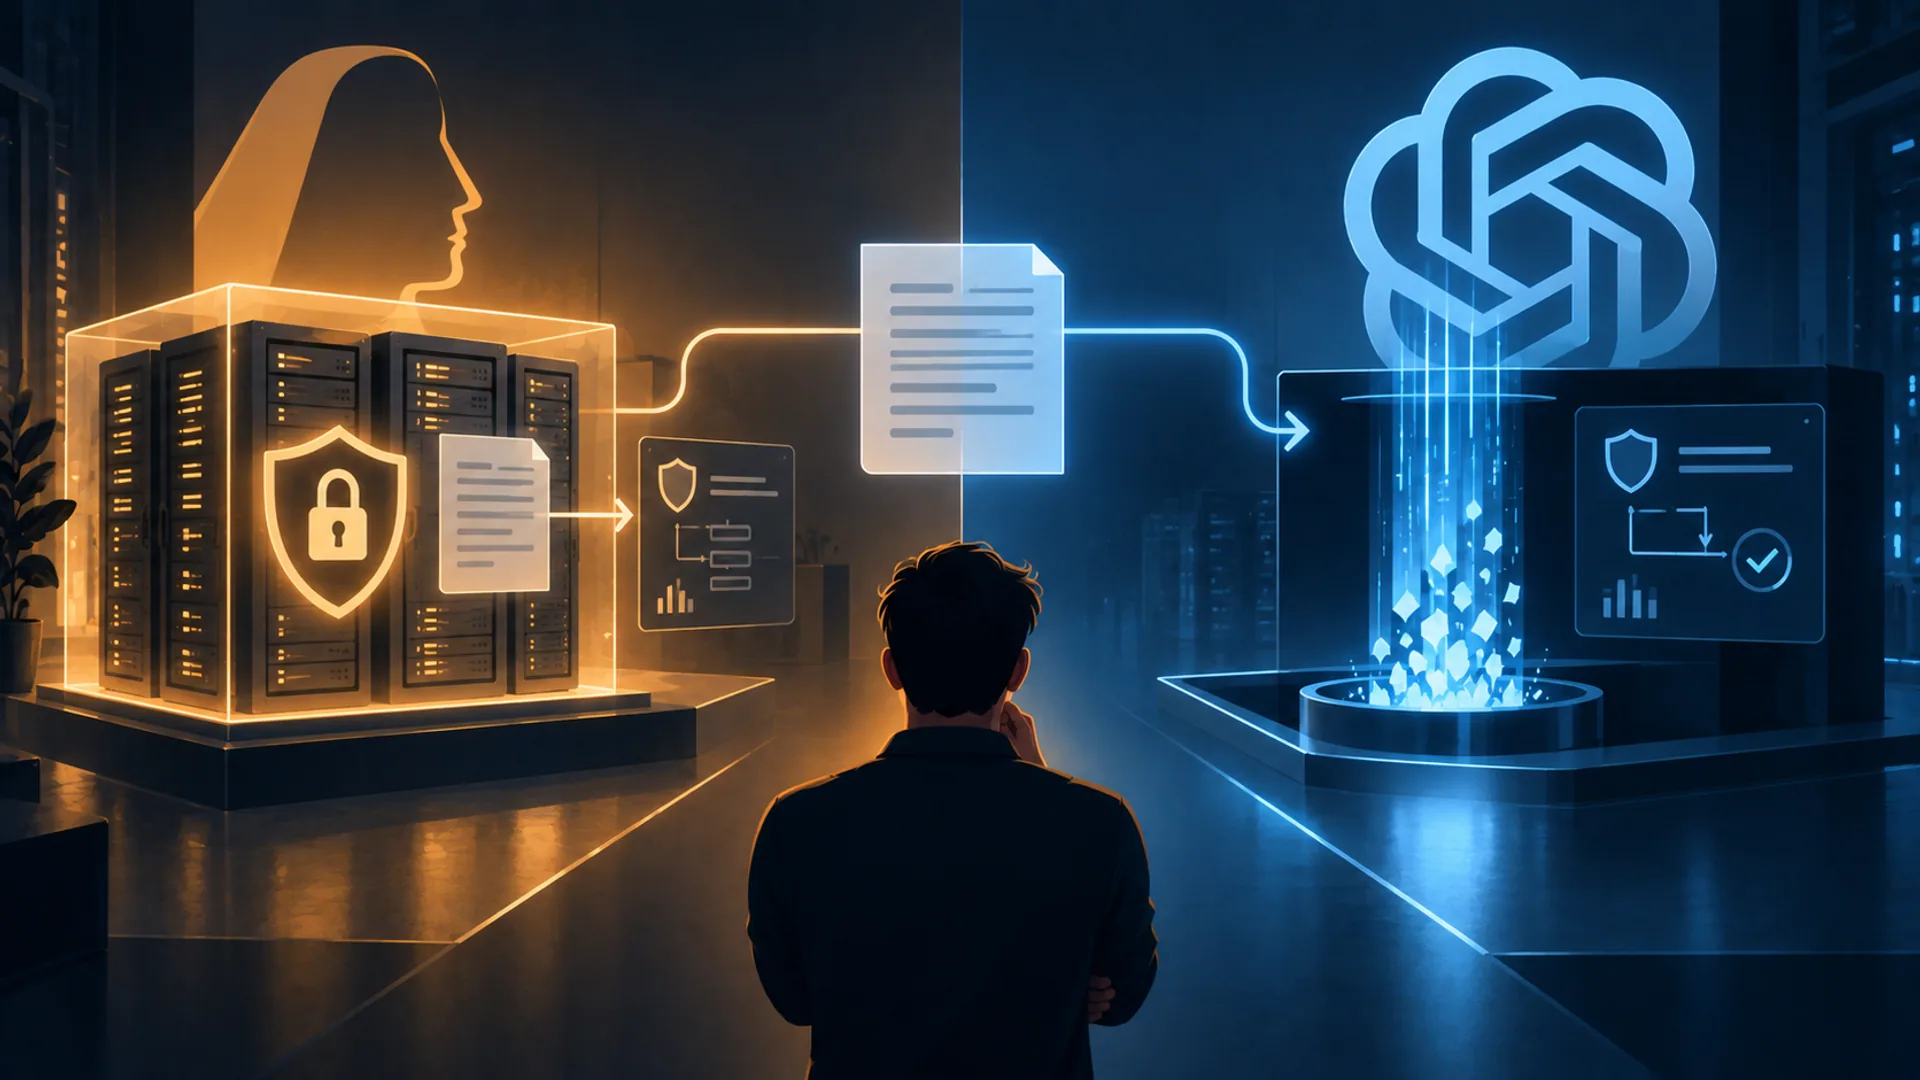
- The new program, Enterprise Frontier Safeguards (EFS), reverses the location, not the retention window
- Data still gets kept for 30 days, but it now sits on the customer's own servers or a cloud provider they choose, not Anthropic's
What changed at OpenAI:
- Promised zero data retention outright for approved enterprise customers on its most capable models, meaning nothing gets logged in the first place
- Previewed Private Safety Processing (PSP), built to catch abuse patterns spread across many requests without a human ever reading the prompts
| Anthropic (EFS) | OpenAI (ZDR + PSP) | |
|---|---|---|
| Data stored | Yes, 30 days, on customer's own infrastructure | No, zero retention by default |
| Human review | None required by default | None, except where federal law requires it |
| Rollout | Phased, starting this fall | Available now to approved businesses |
Both companies describe the same underlying mechanism behind the scenes. Automated software watches requests over time and flags suspicious patterns. But that framing skips a distinction worth sitting with.
"Our employees can't see it" and "our systems can't see it" are different claims. To scan encrypted data for misuse patterns, software has to unlock and read it somewhere, regardless of whose servers it sits on.
Why it matters more for some businesses than others:
- The stakes are highest for exactly the customers these programs are trying to win over: law firms, hospitals, banks, anyone in a regulated industry
- A prompt might contain something that legally cannot leave a specific jurisdiction or a specific server
- "We won't train on your data" and "we don't have your data" are not interchangeable protections, even if both get pitched with the same reassuring paragraph
- Data sitting on a server, whoever controls it, can still be reached by a subpoena or exposed in a breach
Neither company has published the technical details behind how their monitoring actually works, and neither has released an independent audit of the design. Until that happens, "we protect your privacy while still catching misuse" is a claim being sold on trust, not shown in the architecture.